Penetration testing · Incident response · Security program advisory
Security testing that closes the path of least resistance.
DR Data Security is a principal-led cybersecurity consultancy with nearly 30 years of practitioner experience behind it, more than 20 of them in cybersecurity consulting. Penetration testing, incident response, and advisory work for banks, insurers, airports, utilities, and the firms that run them, across the US, the Caribbean, and Latin America. Led by David Rippel, CISSP held continuously since 2003.
The approach
Understand. Test. Verify. Remediate. Defend.
Every engagement follows the same five steps. Select a step to see what the client receives from it.
Proposed project timeline, typical four-week engagement
Fixed price. Consulting days are never a billing basis.The defensive lens
CIA protects data. RVI closes pathways.
The classic CIA triad describes what to protect. The RVI lens describes how attackers get in and what closes the route. Both are used on every engagement.
How maturity is reported
One scale, stated plainly, on every program assessment.
Tabletop and program assessments report where the organization sits today and what the next level requires. Select a level.
Services
Six things DR Data Security does well.
Quality over volume. Select a service to see what the client receives.
What each engagement delivers
| Deliverable | Pen test | Tabletop | Incident response | vCISO | Program |
|---|---|---|---|---|---|
| Executive report in plain conclusions | Yes | Yes | Yes | Quarterly | Yes |
| Technical report with evidence per finding | Yes | No | Yes | No | Yes |
| Findings tracked in the client portal | Yes | Yes | Yes | Yes | Yes |
| Fixes re-tested during the engagement | Yes | No | Eradication verified | No | No |
| Detection use cases for the security team | Yes | Yes | Yes | No | No |
| Readiness rating on the five-level scale | No | Yes | No | Yes | Yes |
| Recommended sequence, client decides each item | Yes | Yes | Yes | Yes | Yes |
| Risk register maintained against business priorities | No | No | No | Yes | Yes |
When something has already happened
How DR handles an incident.
Two dates matter and are never collapsed into one: when the attacker got in, and when anyone noticed. Everything after that is measured.
After the report
The test ends. The tracking does not.
A penetration test is a snapshot. DR keeps the picture current with a recurring posture update: the organization's external security rating, the ratings of its key vendors, and whether last quarter's findings are still closed.
- External rating, month over monthThe organization's score and its industry average, with the specific exposures that moved it.
- Third-party riskThe same rating for key vendors and partners, so a supplier's weak posture is on the agenda before it becomes the organization's incident.
- Findings statusWhich findings are closed, which are accepted as risk, and which have quietly reopened.
- Scan results in the portalExternal and cloud configuration scans on a schedule, with new hosts flagged for approval rather than silently added.
- A 30-minute callThe principal walks through it. The written update stands on its own for anyone who missed the call.
Platform
Two tools DR built because nothing on the market did the job.
Both are DR's own work, reused across every engagement and branded for the client or the partner. Clients get read-only access to their own data and nobody else's.
Vulnerability management portal
One place for everything an engagement produces: discovered hosts awaiting approval, findings with evidence and status, external posture against the industry, and the reports themselves. Replaces spreadsheets, shared scanner logins, and PDF attachments.
- Scope the client controlsNew hosts land as proposed; the client approves before anything is tested.
- Findings that stay aliveTriaged, deduplicated, and tracked through fix, re-test, and acceptance.
- Posture and reports togetherExternal rating, industry comparison, and every report, shareable with the board.
- AI-assisted, human-verifiedRemediation guidance and prioritization drafted by AI, checked by the tester.
Cyber Risk Ontology
An AI-assisted risk management platform that connects what the tests find to the controls that exist and the business risks that matter. Leadership sees one picture; the security team sees exactly which finding moves which risk.
- Built on RVIRisks, visibility, and identities are first-class in the model, not tags on a spreadsheet.
- Connectors, not uploadsScanners, cloud posture tools, and the DR portal feed it directly. Modules are reusable across clients; a client pays only to connect its own.
- Decisions, recordedAccept, treat, or defer, with an owner and a review date. The register is the audit trail.
- Branded per client or partnerA demo tenant with the organization's own branding is a short conversation away.
What a DR report looks like
Written for the board. Backed by the evidence.
Every engagement closes with an executive report in plain conclusions and a technical report the security team can act on. Illustrative sample, details redacted.
The external perimeter held against every direct attack attempted.
One internal pathway from a standard user account to domain administrator was found and closed during testing.
The security awareness training program is effective. Reported phishing attempts were acted on within minutes.
| ID | Finding | Severity | Status |
|---|---|---|---|
| F-01 | Kerberoastable service account with domain admin membership | High | Remediated, re-tested |
| F-02 | Legacy authentication enabled on [redacted] tenant | High | Remediated, re-tested |
| F-03 | Missing rate limiting on customer portal login | Medium | Accepted as risk, owner named |
| F-04 | Verbose error disclosure on [redacted] API | Low | Remediated, re-tested |
| F-05 | TLS configuration below current baseline | Info | Scheduled by client |
Each finding carries evidence, likelihood, impact, and a detection use case for the security team.
Free tools
Useful before anyone talks to a human.
Small, honest checks that run from the browser or inside the organization's own tenant. No sign-up, no data retained.
Questionnaires
Ten minutes now saves a scoping call later.
Each one produces something useful on its own. If a conversation follows, it starts with the answers already in hand.
Partners
Delivered with partners clients already trust.
Much of DR's work reaches clients through managed service and technology partners. The partner owns the relationship; DR brings the testing, response, and advisory depth. The people and the standards are the same either way.
 Florida and the Southeast US
 Caribbean financial services and infrastructure
 The Bahamas
 Insurance and title
 South Florida
 vCISO programs and emergency response
Partner names and marks belong to their owners and appear with permission.
Sectors and regions
Built for regulated, high-consequence environments.
Long-standing relationships with banks, central banks, regulators, and credit unions on both sides of the Florida Straits, alongside insurers, airports, utilities, and hospitality groups.
How DR works
What working with DR Data Security looks like.
| A typical test | DR Data Security | |
|---|---|---|
| Who does the work | Scoped by sales, tested by a bench, presented by an account manager | The principal scopes it, tests it, writes it, and presents it |
| Findings | Scanner output with a severity attached | Every finding verified by hand, with evidence, likelihood, and impact |
| During the test | Findings held for the final report | Fixed and re-tested during the window wherever the client allows |
| What good looks like | A list of problems | Positive observations recorded alongside findings, so the board sees what held |
| Recommendations | A mandated remediation plan | Recommended sequence; the client decides, and accepting a risk is a valid outcome |
| After the report | See you next year | Detection use cases handed to the security team, and the portal stays open |
Team
A small team, chosen on purpose.
Senior people on every engagement. Associates join as the scope requires, never as a substitute for the principal.
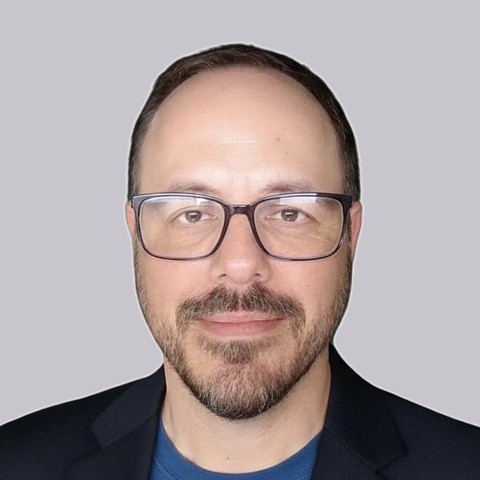
Where DR is going
Building the platform, not reselling someone else's.
Three-question self-check
Can the organization answer these today?
The three questions behind the RVI lens. An honest no on any of them is where most engagements start.
Insights
Short, practical, written from real engagements.
One new piece a month. No vendor pitches, no recycled headlines. All insights
Contact
Start a conversation.
Most engagements begin with a 30-minute scoping call. No sales funnel, a direct line to the principal.
It landed in DR's leads channel and the principal replies personally, usually the same business day.